AI · CYBERSECURITY · COMPLIANCE

Protect your business.
Govern AI.
Stay compliant.

Fractional AI, Cybersecurity & Compliance leadership for regulated and data-sensitive businesses. IusSec helps organizations protect sensitive information, establish responsible AI governance and build practical compliance programs — without the cost of hiring multiple full-time executives.

$497Founding Florida Client Rate
~25Control Areas Assessed
90dPrioritized Roadmap
Fractional AI Leadership· Cybersecurity Governance· FTC Safeguards Rule· WISP· HIPAA Security· AI Governance· Executive Assessment· Vendor Risk· Where Law Meets Intelligence· Fractional AI Leadership· Cybersecurity Governance· FTC Safeguards Rule· WISP· HIPAA Security· AI Governance· Executive Assessment· Vendor Risk· Where Law Meets Intelligence·
Cyber riskSensitive client information, third-party vendors, remote access, cyber insurance requirements and increasingly sophisticated attacks create risks small and mid-sized organizations cannot ignore.
AI adoptionEmployees are already using ChatGPT, Copilot, Gemini and other AI platforms — often without formal policies, risk assessments or clear governance.
The differenceThe problem is not simply technology. It is governance.
The problem

Your business is changing faster than your governance.

🛡️
Cyber Risk
Sensitive client information, third-party vendors, remote access, cyber insurance requirements and increasingly sophisticated attacks create risks that small and mid-sized organizations cannot ignore.
⚙️
AI Adoption
Employees are already using tools such as ChatGPT, Copilot, Gemini and other AI platforms — often without formal policies, risk assessments or clear governance.
✓
Compliance
Regulatory requirements, client security questionnaires and contractual obligations increasingly require documented policies, controls and evidence.
What we do

Three critical responsibilities. One executive partner.

Protect
Cybersecurity & Risk
Cyber risk assessment
Security governance
Risk management
Third-party risk
Incident readiness
Cyber insurance readiness
Executive security oversight
Govern
AI Governance
AI inventory
Shadow AI discovery
AI acceptable-use policies
AI risk assessment
Vendor AI governance
Human oversight
AI adoption strategy
Comply
Compliance
FTC Safeguards Rule
Written Information Security Plan (WISP)
HIPAA
Security policies
Client security requirements
Vendor governance
Evidence and documentation
Requirements depend on your organization, activities and regulatory exposure.
Entry product

Know where you stand before deciding what to fix.

Executive Cyber, AI & Compliance Assessment — a structured, sector-specific review of your organization's risk posture.

01Assess — complete a structured sector-specific assessment covering approximately 25 control areas.
02Expert Review — your responses and supporting information are reviewed by IusSec.
03Executive Scorecard — receive scores across Security · AI · Compliance.
0490-Day Roadmap — prioritized recommendations based on risk, impact and urgency.
05Executive Review — a 30-minute meeting to discuss findings and priorities.

This is a professional paid diagnostic, not a free consultation.

$497
Executive Cyber, AI & Compliance Assessment
Founding Florida Client Rate · Regularly $997
Start My Assessment — $497 →
100% of the Assessment fee is credited toward your first month if you move forward with an Executive Partnership.
First 5 qualified organizations Sector-specific assessment Executive Scorecard + 90-Day Roadmap
Executive partnership

Executive expertise without three executive salaries.

Hiring senior leadership across cybersecurity, AI and compliance can be prohibitively expensive for a growing organization. IusSec provides integrated fractional leadership across these functions — a Fractional AI, Cyber & Compliance Executive.

Core
$2,500/mo, from
Typical profile: 6–20 employees
Designed primarily for smaller regulated organizations.
Recommended
Executive
$4,500/mo, from
Typical profile: 21–50 employees
Recommended for organizations with greater operational, regulatory or data complexity.
Executive+
$7,500/mo, from
Typical profile: 50+ employees
For organizations with more complex environments, multiple locations, larger teams or greater regulatory exposure.

Final scope and pricing depend on complexity, regulatory exposure and required services.

What's included

A dashboard, not just a report.

Monthly executive governance meeting
Updated risk and action roadmap
Security, AI and compliance oversight
Policy development and maintenance
Vendor / third-party risk oversight
Team training and executive reporting
Priority advisory access with a defined response SLA
We do not replace your IT provider. IusSec provides governance, oversight, risk management and executive direction. Your internal IT team or MSP can continue implementing technical controls.
Organization Risk Posture
Security72/100
AI Governance41/100
Compliance64/100
HIGHPriority
3Critical Findings
7Recommended Actions
Industries

Built for organizations trusted with sensitive information.

Healthcare
HIPAA security, sensitive health information, cyber risk, third parties, AI governance.
Law Firms
Client confidentiality, sensitive documents, AI use, vendor risk, security governance.
Financial & Mortgage
Sensitive financial information, cybersecurity, third-party risk, regulatory requirements.
Insurance
Sensitive client data, cyber risk, vendor governance, AI use, compliance.
About IusSec

The team behind every engagement.

IusSec is an independent advisory practice specializing in AI governance, cybersecurity, risk and regulatory compliance — with a technical-legal core and a network of specialists brought in according to the scope of each engagement.
United StatesCybersecurity · AI Governance · Compliance
European UnionAI Governance · AI Act · ISO/IEC 42001
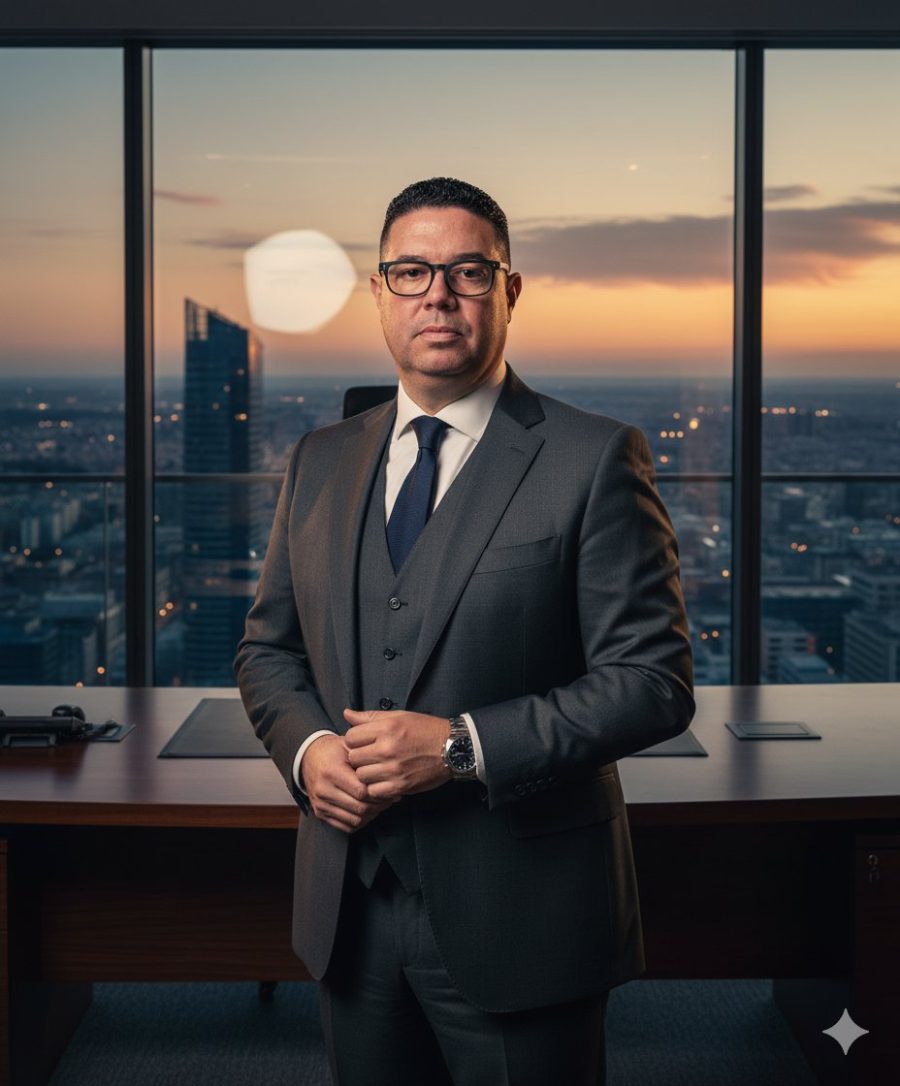
Yonathan Rivas
Yonathan Rivas
Managing Partner · GRC & Information Security

Twenty years in IT, infrastructure and information security. Computer Engineer with officially recognized equivalency in Spain, currently completing a Master's in Cybersecurity & Privacy and a Law degree. He leads engagements across AI governance, information security, data protection and regulatory compliance.

LinkedIn
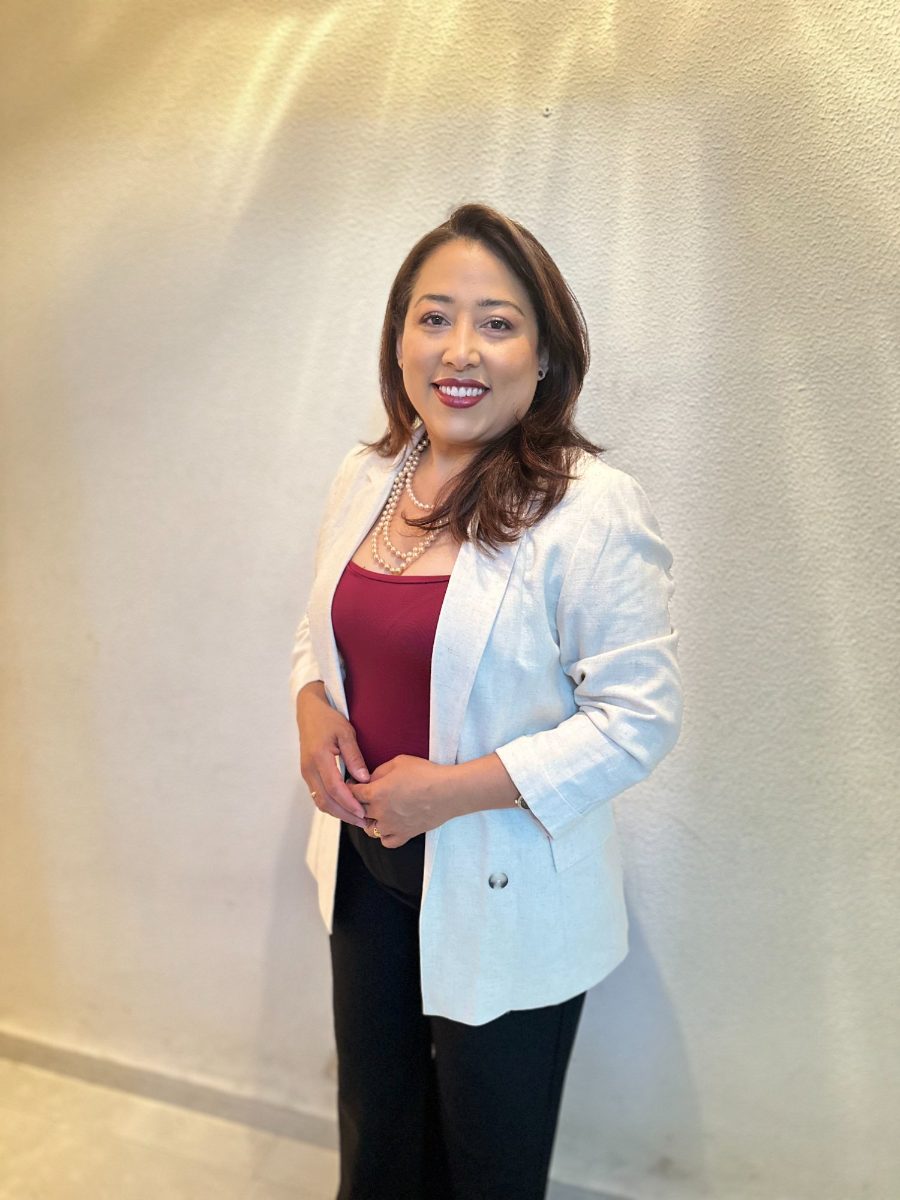
Luiani Rivero Añez
Luiani Rivero Añez
Communications & Brand Director

Social communicator with twenty years in radio, print and television. She leads the firm's positioning, brand and communication, translating technical and regulatory complexity into language executives and boards can act on.

LinkedIn

Governance for an AI-driven world.

Protect. Govern. Comply. Start with the Executive Assessment — a scored, prioritized view of where your organization stands today.

Founding Florida Client Rate · First 5 qualified organizations